Should You Be Concerned About Employees Using AI?
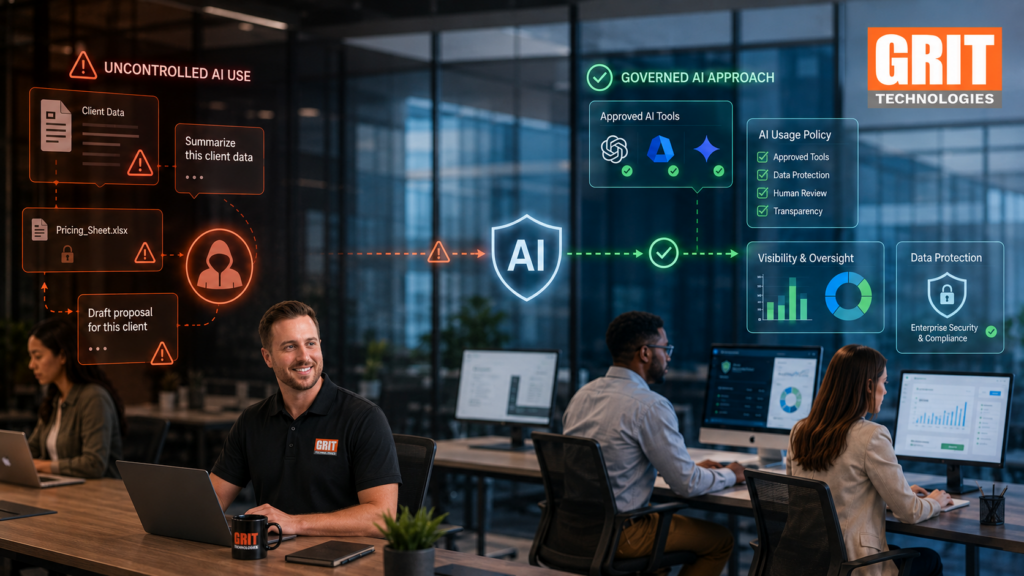
Your employees are already using AI. They’re pasting client notes, pricing details, contracts, and process documents into tools most leaders have never reviewed or formally approved. They’re doing it because it makes their jobs easier. And in most companies, no one in IT or leadership has a clear picture of what information is leaking out of the organization.
That gap is where the real risk hides. Not in some distant future of rogue algorithms, but in the everyday decision to drop sensitive information into a system you don’t control. The productivity upside is real. The exposure is also real. The companies that get this right stop treating AI as a free productivity tool and start treating it as a governance and risk issue that needs deliberate handling.
Here’s how to tell where your organization actually stands.
The Quiet Risk Most Leaders Don’t See Yet
Shadow AI isn’t dramatic. It doesn’t crash systems or light up dashboards. It just moves data outside your organizational boundaries one prompt at a time. Once that information is in a public model, you lose control over how it’s stored, used, or potentially exposed. Compliance obligations don’t care that the employee was trying to be helpful. Neither do clients or regulators.
The bigger problem is that traditional IT controls were never built for this. Firewalls and endpoint protection don’t stop someone from copying text into a browser window. That leaves many organizations relying on hope and employee judgment—the perfect set up to create expensive surprises later.
Five Questions Every Leader Should Ask Right Now
Use these to pressure-test your current posture. Honest answers usually reveal whether you’re governing AI or just hoping it stays contained.
1. Do we know which AI tools employees are using? If you can’t answer this with confidence, you already have shadow AI. Data is leaking without an audit trail or contractual protection.
- Strong answer: “We maintain a current inventory of approved tools, watch for high-risk patterns, and give people sanctioned alternatives that meet our standards.”
- Red flag: “We assume people follow the handbook” or “We blocked a few consumer sites and called it good.”
2. Is there a clear, written policy that employees have acknowledged? Vague rules create compliance gaps that surface during audits or incidents—not before.
- Strong answer: “We have a practical, short policy that defines approved tools, prohibited data, and what to do when someone isn’t sure. Staff have seen it and acknowledged it.”
- Red flag: “It’s covered under our general technology policy” or “We’ll write one when we have time.”
3. Can we control what data is allowed into external AI systems? Public tools often retain prompts. Proprietary pricing, client details, or internal processes that leave your environment are hard to get back.
- Strong answer: “We have clear data classification rules and practical guidance on what stays inside. High-risk categories are explicitly off-limits.”
- Red flag: “We trust people to know what’s sensitive.”
4. Is our current IT or security partner treating AI as a real risk domain? If AI is still viewed only as a productivity discussion, the security and compliance pieces are probably lagging.
- Strong answer: “Our partner helps us inventory usage, set guardrails, train staff, and fold AI risk into our broader security and compliance work.”
- Red flag: “They handle tickets and patches. AI is something the business side is figuring out.”
5. Do we have a process for approving new AI tools before they spread? New tools appear weekly. Without a simple review path, risk accumulates faster than leadership can respond.
- Strong answer: “We have a quick review process that balances speed with security, data handling, and compliance checks.”
- Red flag: “Anyone can sign up for whatever helps them move faster.”
A Practical Path Forward This Month
You don’t need a six-month initiative to reduce your biggest exposures. Start here:
- Ask department leads what AI tools their teams are already using (formally or not).
- Identify the two or three most sensitive data categories that you need to keep out of external models.
- Publish a short acceptable-use statement and have employees acknowledge it.
- Decide which tools are approved and provide at least one controlled alternative for common use cases.
- Schedule a 30-day review to adjust based on real usage.
This sequence gives you visibility and basic guardrails without grinding work to a halt.
The organizations that handle AI well don’t ban it. They govern it. They keep the productivity gains while reducing the chance that helpful employees accidentally create the next compliance or security problem.
Where GRIT fits
If people are already using AI and you can’t see which tools, or what they’re putting into them, a policy by itself won’t close the gap.
GRIT Technologies helps growing companies get a handle on AI use, instead of leaving it as a side conversation. Find out what’s already in use. Write a short policy people can actually follow. Give them an approved option for the work they’re doing anyway. The aim is plain. Keep the speed. Cut the easy ways sensitive information leaves the building.
Ready to see where you actually stand? Contact GRIT. No hype. Just a practical look at the risk and a workable path.
FAQs
Is banning all AI tools a realistic solution?
Almost never. A ban pushes the work underground, and you lose whatever visibility you had. Clear rules and at least one approved option beat a policy nobody follows.
How serious is the data risk from everyday AI use?
Serious enough to treat it as a real issue, not a future one. Once client notes, pricing, or internal documents go into a public tool, you don’t control how that information is stored or reused. “They were just trying to move faster” doesn’t help with a client or an audit.
Does our existing cybersecurity program already cover this?
Not fully. Firewalls and endpoint protection don’t stop someone from pasting text into a browser. This needs a short policy, a clear line on what data stays inside, and someone watching which tools people are actually using.
Who should own AI governance — IT, legal, or the business?
It’s shared, but someone has to lead. The setups that work are the ones where IT and security write rules the business can follow, and leadership is willing to back them.
What’s the fastest way to cut the immediate exposure?
Ask department leads what tools people are already using. Name the two or three kinds of data that shouldn’t leave the building. Publish a short acceptable-use note and have people acknowledge it. Then give them one approved option for the work they’re already doing.